
Table of Contents
“This article contains content that has been artificially generated or manipulated using AI tools.”
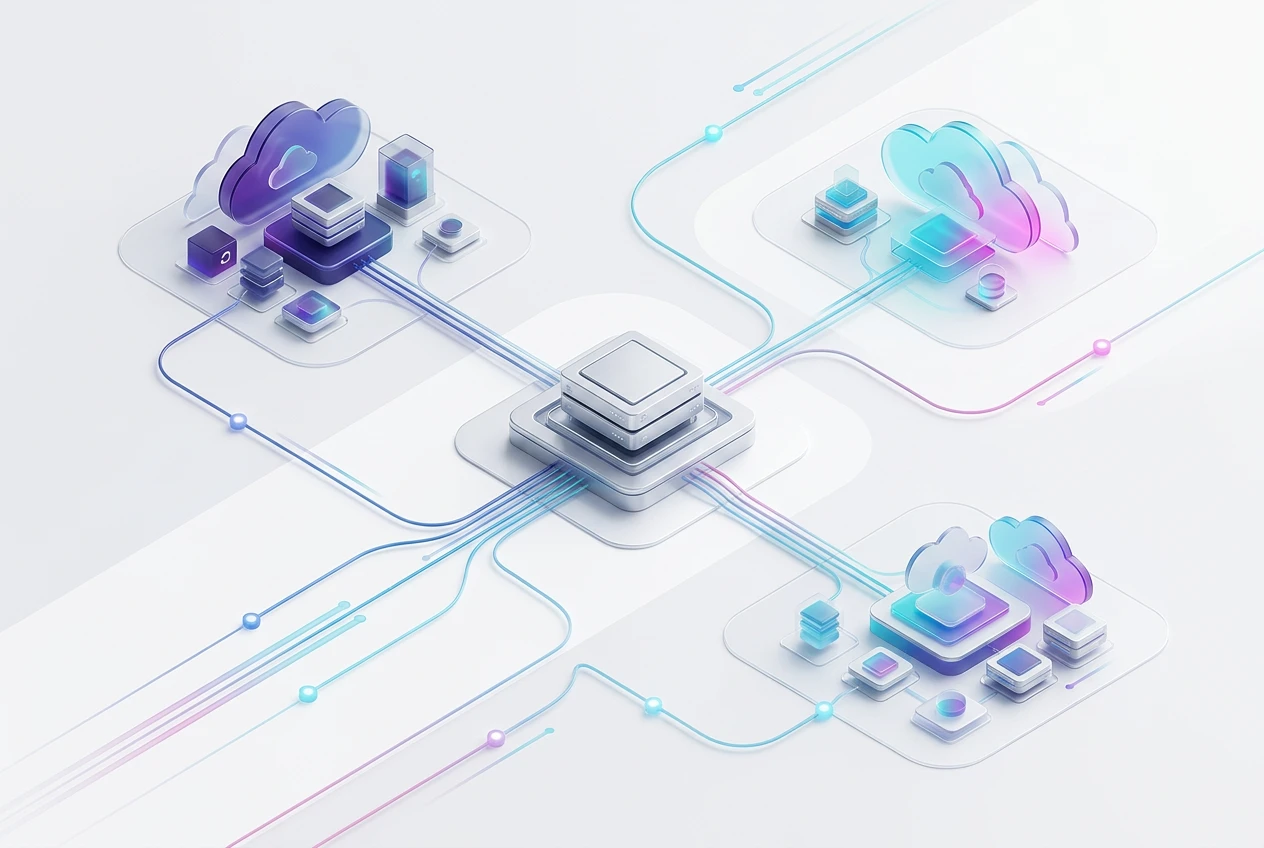
Comparing multi-cloud vs hybrid cloud is not a choice between two opposing architectures. Hybrid cloud connects public-cloud services with private, on-premises, or edge environments, while multi-cloud intentionally uses services from more than one public-cloud provider. An organization can therefore be both hybrid and multi-cloud.
The more useful question is which workloads need to run where, which providers are genuinely required, and whether the organization can govern, secure, connect, and fund the resulting operating model. This guide compares both approaches across portability, data residency, resilience, networking, governance, skills, and cost before mapping them to common enterprise scenarios.
Key Takeaways
- Coexistence over exclusion: Hybrid cloud and multi-cloud architectures are not mutually exclusive, and some organizations operate hybrid multi-cloud environments when both sets of requirements apply.
- Distinct drivers: Hybrid deployments are typically driven by data residency and workload placement constraints, whereas multi-cloud strategies leverage specific capabilities across multiple public-cloud ecosystems.
- Earned outcomes: Application portability, operational resilience, and reduced vendor lock-in are deliberate design outcomes rather than automatic benefits of these architectures.
- Simplicity first: Organizations should select the least complex architecture that satisfies their operational, regulatory, and business requirements.
Multi-Cloud vs Hybrid Cloud at a Glance
This multi-cloud vs. hybrid cloud matrix compares both architectures across core operational dimensions to guide infrastructure selection. It highlights key trade-offs in control, compliance, and engineering overhead. Use these insights to align your cloud strategy with organizational capabilities.
| Decision factor | Hybrid cloud | Multi-cloud |
|---|---|---|
| Core architecture | Connected private infrastructure and public-cloud capacity; assess workload placement and integration boundaries | Services distributed across multiple public-cloud providers; assess portability and cross-provider dependencies |
| On-premises dependency | Often includes private, on-premises, or edge infrastructure, but the private side does not have to be a traditional data center | Does not require on-premises infrastructure; verify that provider services cover all workload and data needs |
| Public-cloud vendors | May use one or more public-cloud providers alongside private/local infrastructure | Uses multiple public-cloud providers; compare overlapping services, interfaces, and operational responsibilities |
| Primary driver | Data control and placement flexibility; choose when local infrastructure must remain part of the operating model | Service diversity and provider choice; choose when different providers offer distinct workload capabilities |
| Vendor lock-in | Can preserve control over selected workloads, but may still create dependence on private-platform tooling, cloud services, integrations, or operational processes | Can diversify dependence on one provider, while still creating lock-in to proprietary services across multiple clouds |
| Portability | Requires deliberate architecture and integration; movement between private and public environments is not automatic | Requires deliberate abstractions, data architecture, identity, networking, and deployment choices; using several clouds does not itself make workloads portable |
| Data residency | Provides local placement and direct control for data that remains on private infrastructure; map legal and operational location requirements | Uses provider regions for data placement; confirm available regions, replication behavior, and cross-provider transfer paths |
| Security and governance | Policies must span private/local and public-cloud environments, often with different identity, logging, security, and lifecycle controls | Requires consistent controls across providers; compare identity, logging, policy enforcement, and audit workflows before standardizing |
| Networking | Depends on dedicated WAN or VPN links between local and public environments; check latency, bandwidth, redundancy, and routing ownership | Cross-cloud connectivity may be unnecessary for isolated workloads but becomes complex when systems exchange data or depend on one another |
| Resilience | Can combine local recovery capabilities with public-cloud resources; test failover across the private-public boundary | Can distribute workloads or recovery paths across providers; test cross-provider failover, data synchronization, and operational coordination |
| Operational complexity | Requires hardware, facilities, private-platform, and public-cloud management; assign ownership for the full connected environment | Requires multi-platform management across providers; standardize tooling, skills, incident response, and service visibility |
| Cost governance | Must govern both capital and operating costs, including local infrastructure and public-cloud consumption; define allocation and refresh controls | Must govern operating costs across vendors; reconcile billing, data-transfer charges, commitments, and workload placement decisions |
The Most Important Difference: Workload Placement vs Provider Strategy
To clarify the multi-cloud vs hybrid cloud distinction, look beyond standard definitions to the core driver of your infrastructure design. A hybrid cloud strategy addresses workload placement, specifically asking whether data or applications must remain on-premises, local, or at the edge while interoperating with public cloud resources. Conversely, a multi-cloud strategy focuses on provider diversification, asking whether there is a deliberate business or technical reason to deploy workloads across multiple public cloud vendors. When an organization faces both sets of requirements, the resulting architecture becomes a hybrid multi-cloud design that spans multiple environments. Once workload-placement requirements are clear, teams that still need to choose between major public-cloud ecosystems can use our AWS vs Azure vs Google Cloud comparison to evaluate provider fit.
Vendor Lock-In and Portability: Do Not Treat Them as Synonyms
While distributing workloads across multiple public clouds reduces single-provider dependence, it does not guarantee application portability because organizations often couple applications to proprietary databases or message queues on each platform. Improving portability may involve containers or Kubernetes where appropriate, Infrastructure as Code, open interfaces and data formats, and carefully chosen abstraction boundaries. However, forcing every workload onto the lowest common denominator can prevent teams from using valuable provider-native services. Teams should only mandate portability where switching or dual-running offers clear business value, balancing migration flexibility against the overhead of custom abstraction layers.
Data Residency, Security, and Governance
Hybrid cloud architectures address residency by keeping selected data and compute local, which requires extending existing identity, policy, logging, inventory, vulnerability management, and audit controls to the public cloud. Conversely, multi-cloud strategies introduce provider-specific IAM, policy, and security frameworks, requiring teams to normalize identity, logging, secrets, configuration, and posture across differing regional control models to prevent governance drift. Neither architecture inherently guarantees compliance, and organizations must not assume that on-premises environments are automatically compliant or that multi-cloud setups are inherently safer. When evaluating multi-cloud vs hybrid cloud architectures, security teams must validate their operational capabilities before selecting either model.
Networking, Data Movement, and Resilience
Hybrid architectures rely on private connectivity, direct links, or VPNs to manage latency, bandwidth, routing, DNS, and identity dependencies during data synchronization. Conversely, multi-cloud networking requires managing cross-provider latency, service discovery, security inspection, and data-transfer or egress costs that can become material for data-intensive workloads. Deploying across two public providers does not automatically make an application more resilient, as it introduces complex failure modes. When designing for high availability, organizations should validate their actual recovery time objectives before choosing a multi-cloud strategy, as a single-provider multi-region deployment is often simpler and sufficient.
Operational Complexity, Skills, and Cost Governance
When comparing multi-cloud and hybrid cloud, organizations should evaluate total cost of ownership, operating-model complexity, and the skills required to run each environment. Multi-cloud can duplicate platform expertise and tooling when teams lack shared standards; adopting cloud-agnostic control planes can reduce that duplication. Hybrid cloud continues to carry private-infrastructure costs while adding public-cloud operations. Because neither model is inherently cheaper, organizations should use FinOps to maintain cost visibility and prevent billing fragmentation, as compared below.
| Operating Area | Hybrid Cloud | Multi-Cloud |
|---|---|---|
| Platform skills | Requires public-cloud plus private/on-premises/edge expertise | Requires expertise across multiple provider ecosystems, services, IAM models, and networking approaches |
| Tooling & Governance | Must provide visibility and controls across local/private and public environments | Must normalize governance and observability across different provider-native tools |
| Operations | Coordinates connectivity, capacity, patching, lifecycle, and cloud operations across environments | Coordinates common standards while preserving enough provider-specific expertise to operate each cloud correctly |
| Cost Management | Combines private-infrastructure TCO with cloud consumption and migration costs | Must reconcile billing models, tagging, commitments, shared services, and data-transfer costs across providers |
Neither architecture is inherently cheaper. Hybrid cloud retains private-infrastructure costs alongside cloud operations, while multi-cloud can duplicate skills, tooling, and governance unless teams standardize deliberately. FinOps becomes particularly important when costs must be normalized across providers, workloads, and business owners.
Which Architecture Fits Common Business Scenarios?
Evaluating organizational alignment across common operational scenarios helps clarify the optimal architectural path. This comparison table outlines how specific business requirements influence the choice between hybrid and multi-cloud models. Teams should use these patterns to assess their current infrastructure dependencies and confirm the operational constraints that could change the recommendation.
| Scenario | Likely Direction | Why | What to Validate |
|---|---|---|---|
| Regulated or data-sensitive workloads | Hybrid or hybrid multi-cloud, depending actual requirements | Selected workloads or data may need private/local placement, while suitable services can still run in public cloud environments | Residency, data flows, encryption and keys, IAM, audit controls, eligible providers/regions, recovery requirements |
| Legacy modernization involving coupled applications or data stores | Hybrid, often as a transition architecture during staged modernization | Supports incremental modernization without requiring tightly connected legacy systems to move at once | Test application and database latency tolerances, dependency sequencing, integration behavior, and rollback procedures |
| Geographic or provider resilience | Multi-region single-cloud or multi-cloud, depending the failure model | Multi-cloud may be justified when provider concentration itself is an unacceptable risk; otherwise, multi-region resilience within one provider can be simpler | RTO/RPO, replication, failover, DNS, identity, data consistency, provider-independent dependencies, DR testing |
| AI and data workloads | Workload-specific: hybrid, multi-cloud, or both | Sensitive/source data may stay local while cloud services provide analytics or AI capabilities; multiple clouds may also provide differentiated models, accelerators, regions, or data services | Data location, egress, accelerator availability, privacy, latency, model access, pipelines, observability |
| SaaS products seeking a fast, operationally focused launch | Single-cloud, when one provider satisfies product and customer requirements | Minimizes infrastructure complexity and can accelerate market entry by concentrating deployment and operations in one environment | Confirm customer hosting mandates, required regional availability, provider service limits, portability expectations, and the operational cost of later expansion |
Can You Be Hybrid and Multi-Cloud at the Same Time?
Yes, organizations can operate a hybrid multi-cloud architecture, though it should not be the default choice. For example, an enterprise might retain a regulated legacy database in a private data center, host its primary application on Azure, and route data to Google Cloud for specialized machine learning analytics. This model should be adopted only when specific workload requirements demand it, rather than from a desire to appear cloud-agnostic.
Implementing this strategy introduces significant operational overhead, adding complex layers of identity, networking, security, observability, skills, and cost governance. Before proceeding, engineering leaders should validate that their platform teams can manage these multi-provider complexities without degrading system reliability.
When a Cloud Architecture Decision Becomes a Migration and Operating-Model Decision
Choosing an architecture is only the first part of cloud modernization. Implementation may still require workload assessment, migration sequencing, network and security design, Infrastructure as Code, CI/CD, monitoring, and an operating model for the target environment.
Scopic’s work with AIS International Group illustrates this operational side of migration. The engagement included data migration to Azure servers alongside CI/CD, infrastructure security, logging, and monitoring. The relevant lesson is not that Azure or a particular cloud model is universally preferable, but that migration architecture needs supporting controls for delivery, security, observability, and ongoing operations.
Architecture-Selection Checklist
Use this checklist to evaluate your architectural direction against your primary operational drivers, constraints, and fallback options.
| Question | If Yes, it may point toward |
|---|---|
| Must specific workloads or data remain private, local, on-premises, or at the edge? | Hybrid cloud |
| Must private/local systems continuously interact with public-cloud services? | Hybrid cloud |
| Is there a deliberate business or technical reason to operate more than one public-cloud provider? | Multi-cloud |
| Is provider concentration itself an unacceptable business risk that justifies true cross-provider resilience? | Multi-cloud, if the organization can support it operationally |
| Do both private/local placement requirements and multiple-provider requirements exist? | Hybrid multi-cloud |
| Could all requirements be met through one public cloud using appropriate regions and services? | Consider staying single-cloud |
Before adding another environment or provider, define what must remain local, which workloads genuinely require another cloud, what failure scenarios must be covered, where data may reside, how identity and security policies will be governed, and who will operate the resulting environment. If there is no strong answer to why the additional complexity is necessary, do not add it by default.
Conclusion
Hybrid cloud and multi-cloud solve different architecture problems. Hybrid designs are primarily about where workloads and data need to run, while multi-cloud strategies introduce more than one public-cloud ecosystem for deliberate service, geographic, organizational, or risk-management reasons. Some organizations need both; others need neither. The stronger starting point is usually the least complex architecture that satisfies workload, residency, resilience, governance, skills, and cost requirements.
If you need help evaluating cloud architecture or migration options, contact us to discuss your workloads and operating requirements.
FAQ
What is the primary difference in the multi-cloud vs hybrid cloud comparison?
The primary distinction lies in infrastructure integration and provider diversity. A hybrid cloud integrates private infrastructure, such as on-premises data centers or private clouds, with public cloud services to manage workload placement. In contrast, a multi-cloud strategy utilizes services from two or more public cloud providers without necessarily relying on private infrastructure. While hybrid cloud focuses on bridging local control with public scalability, multi-cloud emphasizes distributing workloads across different public vendors to leverage specific proprietary capabilities or geographic regions.
Can an organization implement both hybrid and multi-cloud strategies simultaneously?
Yes. A hybrid multi-cloud architecture combines private, on-premises, or edge infrastructure with services from multiple public-cloud providers. For example, one workload might remain in a private environment while the organization uses Azure for its primary application and another cloud for a specialized analytics service. This can solve legitimate placement and provider requirements, but it also increases identity, networking, security, observability, skills, and cost-governance complexity.
Does a multi-cloud architecture prevent vendor lock-in?
No, distributing workloads across multiple public cloud providers does not completely remove vendor dependency. While it reduces reliance on a single provider, it often introduces new integration challenges at the application layer. Utilizing proprietary services, such as managed databases or specialized analytics tools, binds applications to those specific platforms, while attempting to build completely portable applications using only basic, cross-platform services often increases development overhead. Teams must balance the engineering effort of abstraction against the actual business risk of vendor dependency.
Is a multi-cloud architecture more resilient than a hybrid cloud model?
Not inherently. Multi-cloud can address provider-concentration risk, but resilience still depends on data replication, DNS and traffic management, identity, infrastructure parity, tested failover, observability, and operational runbooks. Hybrid architectures can also support continuity patterns, while many applications can achieve their required availability through multiple regions within one public cloud. The appropriate design depends on the failure scenarios the organization actually needs to withstand.
This article contains content that has been artificially generated or manipulated using AI tools. The article was reviewed and fact-checked by Srbuhi Avetisyan, AI Content Specialist at Scopic Software.
Scopic provides quality and informative content, powered by our deep-rooted expertise in software development. Our team of content writers and experts have great knowledge in the latest software technologies, allowing them to break down even the most complex topics in the field. They also know how to tackle topics from a wide range of industries, capture their essence, and deliver valuable content across all digital platforms.

 Message Scopio